Self-hosted server
Simple CVE Tracker
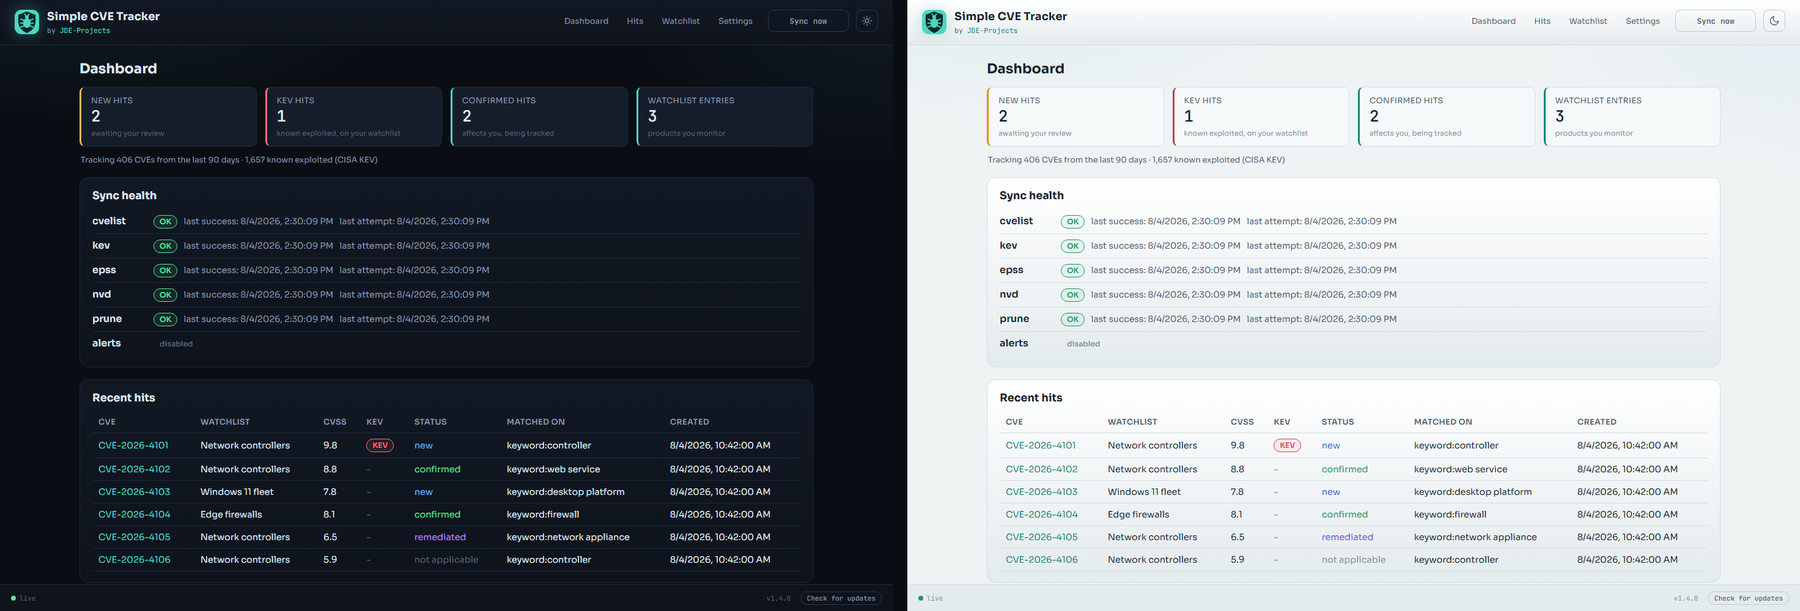
A self-hosted server that watches public CVE feeds and surfaces only the vulnerabilities matching the keywords, vendor-product pairs, and CPE product codes on your watchlists.
Built for
People who track new vulnerabilities for the specific vendors and products they run, without watching the full public feed.
- Match keyword, vendor-product, and CPE product-code watchlists with optional CVSS thresholds
- Flag CISA KEV entries and enrich findings with NVD CVSS, FIRST EPSS, and CWE weakness data
- Show per-source synchronization health and support an immediate manual sync
Get it
Download the source tarball from GitHub Releases, then use Docker Compose, run from Python 3.11+, or install the included systemd service. The site does not select or serve a version-specific artifact.
Verify the download
You can check GitHub’s build-provenance record against the released file.
gh attestation verify simple-cve-tracker-vX.Y.Z.tar.gz --repo JDE-Projects/Simple-CVE-Tracker --signer-repo JDE-Projects/Build-ToolsLicense
PolyForm Noncommercial License 1.0.0. Personal use and evaluation are fine. Commercial use, including use by a business, is not permitted under this license yet.
If your team wants to use a tool at work, see commercial licensing on the support page.