Windows desktop
Simple SFTP Audit Tool
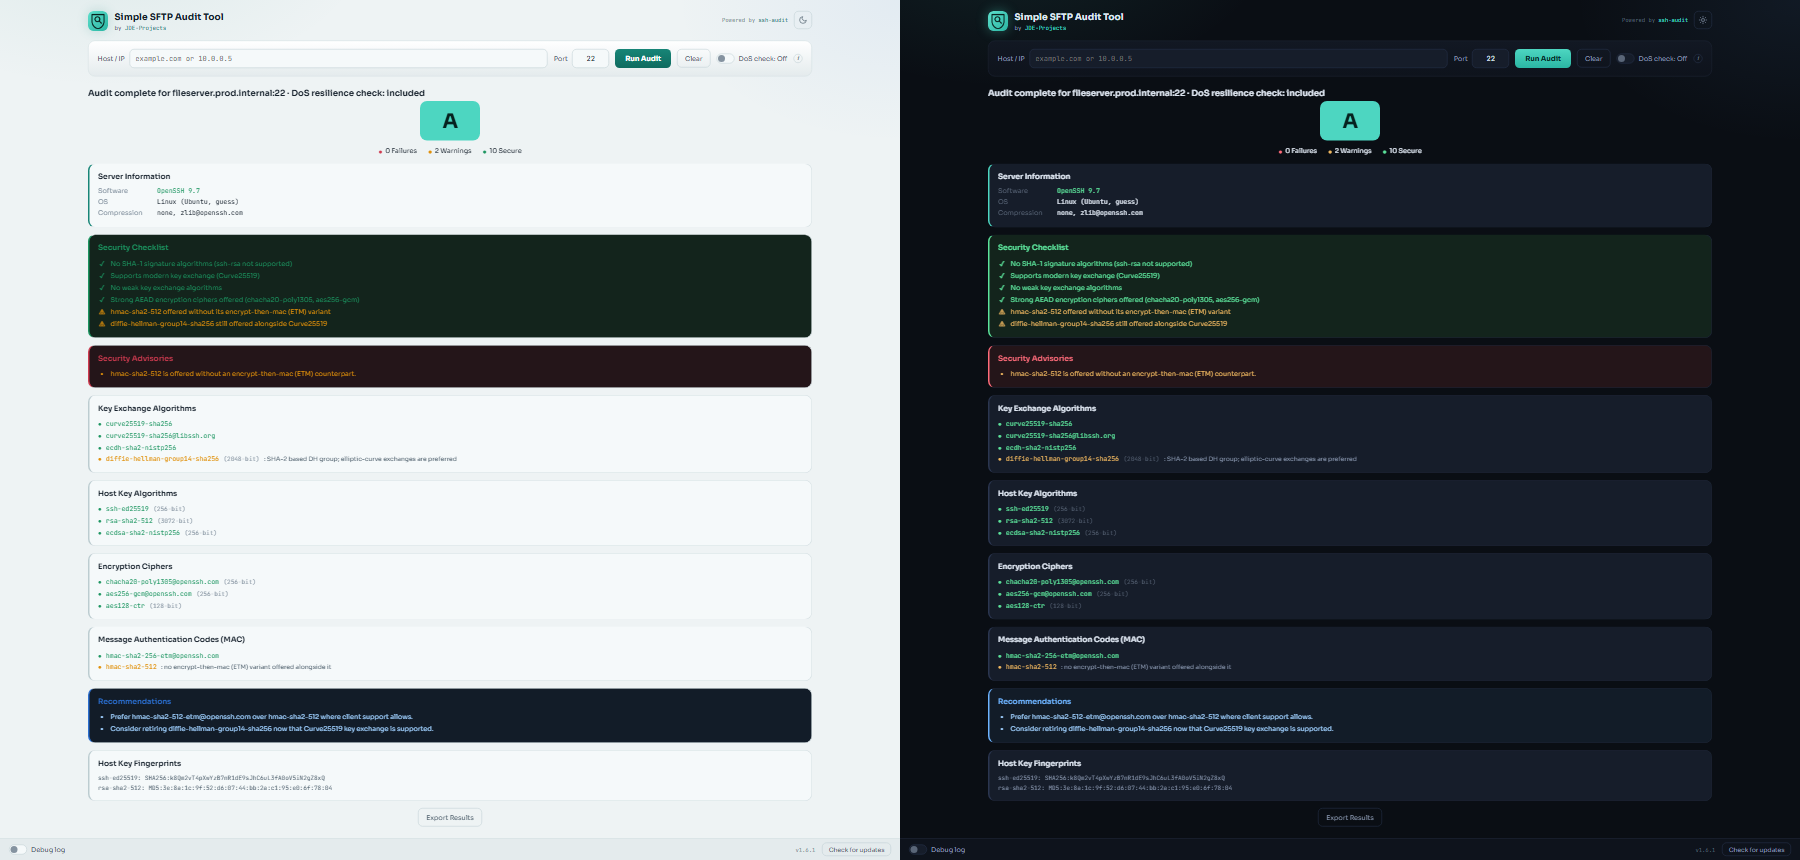
An unauthenticated SSH/SFTP scanner that turns ssh-audit findings into an A+ through F grade and readable report.
Built for
Server owners and IT administrators reviewing SSH and SFTP exposure on systems they are authorized to test.
- Grade findings with failure, warning, and secure-item counts
- Explain weak and modern key exchange, host key, cipher, and MAC choices
- Report the server banner, detected OS, compression, and host-key fingerprints
- Export a plain-text report for tickets or records
Get it
Both formats are on GitHub Releases. The site does not select or serve a version-specific binary.
- Installer (recommended): the file ending in
-setup.exe. Installs just for you with no admin, adds a Start menu shortcut, and removes cleanly from Add or Remove Programs. - Portable ZIP: the file ending in
.zip. No install, good for a locked-down PC or a USB stick. Keep the folder together.
The apps are not signed, so Windows SmartScreen may warn the first time you run one. Choose More info, then Run anyway.
Verify the download
You can check GitHub’s build-provenance record against the released file.
Installer:
gh attestation verify SimpleSFTPAuditTool-vX.Y.Z-setup.exe --repo JDE-Projects/Simple-SFTP-Audit-Tool --signer-repo JDE-Projects/Build-ToolsPortable ZIP:
gh attestation verify SimpleSFTPAuditTool-vX.Y.Z.zip --repo JDE-Projects/Simple-SFTP-Audit-Tool --signer-repo JDE-Projects/Build-ToolsLicense
PolyForm Noncommercial License 1.0.0. Personal use and evaluation are fine. Commercial use, including use by a business, is not permitted under this license yet.
If your team wants to use a tool at work, see commercial licensing on the support page.